
Overview: Google Cloud IAM is the system that manages who can access your projects and what actions they can perform. By using clear rules and specific permissions, it keeps your cloud environment secure. This guide walks you through the core concepts of cloud security, showing you how to set up access management effectively without making your setup overly complex.
01. Introduction
Every junior engineer eventually hits the dreaded error when trying to deploy a container or read a database table: a permission denied response. It is a rite of passage. You think your code is perfect, your configuration is correct, but the system stops you cold. This happens because Google Cloud IAM is sitting in the background, checking if your service account or user identity has the specific badge required to perform that exact action. In the world of cloud computing, this is the first real lesson in operational security.
Beginners often treat IAM like a giant bucket where they dump broad permissions just to get the deployment running. They assign Owner or Editor roles because it is fast and fixes the error immediately. However, this is the fastest way to create a security hole that could cost a company dearly. If a developer accidentally deletes a production database because they were granted "Owner" status to fix a simple network connectivity issue, the cost of that mistake is far higher than the time saved by taking a shortcut.
In a real production environment, you need to be surgical. You grant exactly what is needed for a task and nothing more. This mindset-the principle of least privilege-is the bedrock of modern cloud security. In this article, we will move past the confusion and look at how to structure access control properly. We will cover the core mechanics of identities, roles, and policies. By the end, you will understand how to build secure, scalable, and manageable access layers that satisfy both security auditors and your engineering team.
02. The Logic of Google Cloud IAM
At its heart, Google Cloud IAM answers one simple question: Who can do what on which resource? It breaks this down into three parts. First, you have the identity, which is the who. This is usually a human user, a service account for an application, or a group of employees. Second, you have the role, which is the what. A role is simply a collection of permissions that allow specific actions like creating a virtual machine or reading a storage bucket.
Placement Clients


MSME Companies in UK & US
03. Permission Management Patterns
Managing permissions requires a strategy. You cannot simply manage them randomly as users come and go. The most common pitfall I see in my professional experience is the temptation to use primitive roles like Owner, Editor, or Viewer. These roles are too broad for production. They cover almost every service, meaning a developer who only needs to read logs might accidentally delete a production database or modify firewall rules. Never use these roles in a production environment.
Instead, you should always favor predefined roles or custom roles. Predefined roles are crafted by Google to cover common job functions, like a Storage Object Admin or a Compute Instance Admin. They are safer because they limit the blast radius. If your application only needs to read from a specific bucket, it should have a role that only allows reading from that bucket. This is not just about security; it is about keeping your environment clean and predictable for other engineers working on the same project.
| Role Type | Best For | Security Level |
|---|---|---|
| Primitive Roles | Personal sandboxes | Low |
| Predefined Roles | Common tasks | High |
| Custom Roles | Specific workflows | Very High |
| Basic Roles | Global management | Very Low |
When to Use Custom Roles
Custom roles are your best tool when predefined roles are still too broad. Suppose you have a service that needs to trigger a Cloud Function but should not have any other rights. You can create a custom role that contains only the specific permissions for invoking functions. This follows the principle of least privilege, which is the industry standard for cloud security. It takes more time to set up initially, but it saves hours of troubleshooting and security remediation later.
If you are unsure where to start with custom roles, look at the permissions list for the service you are trying to automate. Most Google Cloud services have a well-documented list of permissions. Pick only the ones you need for the task. If your service fails, you can add permissions one by one. This iterative process is better than granting "Editor" access and hoping for the best. It turns security into a manageable, documented process rather than a guessing game.
04. Production Readiness and Security
In a real company, security is not just about blocking access; it is about visibility. You need to know who is accessing what and when. This is where audit logs become critical. Every time a principal makes a request, Google Cloud logs it. If you ever have an incident, these logs are your source of truth for debugging who initiated the change. Without these logs, you are flying blind during a post-mortem.
Another common mistake is forgetting to prune old service account keys. Keys are long-lived credentials that can be stolen. If a developer leaves the key on a local machine or pushes it to a repository, that key is compromised. The best practice is to avoid using static keys whenever possible. Instead, rely on Workload Identity or internal metadata server authentication, which automatically rotates credentials for you. If you must use keys, treat them like a physical master key to your house-lock them away and rotate them frequently.
The Lifecycle of a Permission Request
When an API call is made, the system performs an authorization check before the request is processed. It checks the IAM policy associated with the resource. If the policy contains the required permission for the identity, the request proceeds. If not, the request is rejected with an error. This happens in milliseconds, but it is the gatekeeper for your entire infrastructure. Understanding this flow helps you troubleshoot "403 Forbidden" errors effectively.
When debugging, I tell my students to look at the IAM Troubleshooter tool. It lets you test a specific identity against a resource and a permission to see if it is allowed. Instead of guessing why an access denial is happening, you can simulate the request. It identifies the exact policy that is missing or the specific role binding that is causing the conflict. It is a lifesaver when you are deep in a production deploy and need a quick answer.
05. Navigating the Complexity of IAM Policies at Scale
Managing access isn't just about clicking buttons in the Google Cloud Console; it is about building a durable framework that survives the growth of your team. When you first start with Google Cloud IAM, it is tempting to assign 'Owner' or 'Editor' roles to everyone just to get things moving. This is a common trap that turns into a security nightmare within months. Instead, think of your organization as a series of concentric circles. At the center, you have the root resources like your billing account or organization node, which should be locked down with ironclad oversight. As you move outward toward specific development projects or staging environments, you can gradually delegate permissions using granular, role-based access.
Scaling your access strategy requires shifting your mindset from individual user management to group-based administration. Never assign a permission to a specific email address if you can avoid it. When a team member leaves or changes roles, manually auditing every single resource they touched is effectively impossible. By grouping users into Google Groups or Workspace identities, you manage access by role rather than by person. If a developer joins the backend team, you simply add them to the 'Backend-Developers' group, and they instantly inherit the precise permissions needed to deploy code to the relevant clusters. This abstraction layer is the secret to keeping your sanity as your cloud footprint expands.
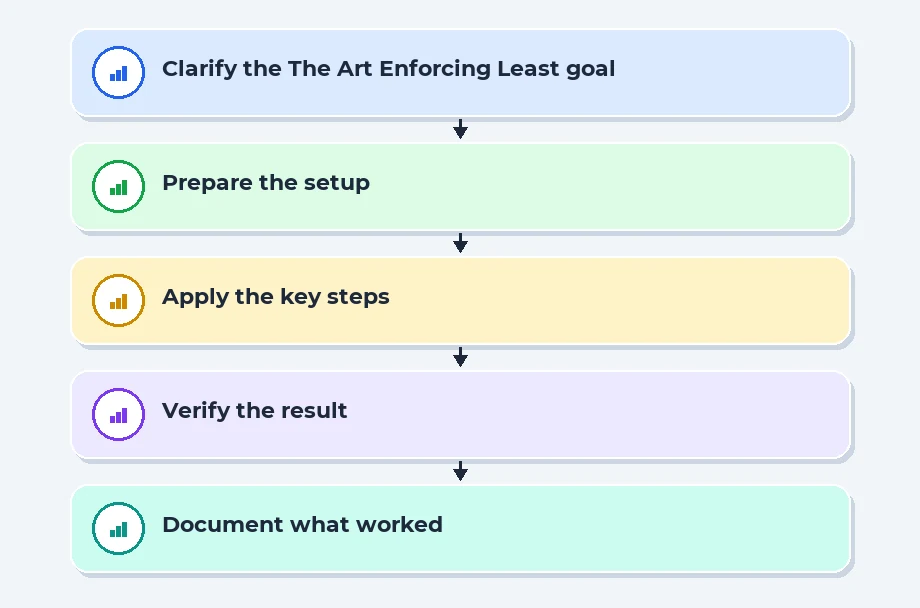
The Art of Enforcing Least Privilege Without Stifling Velocity
The biggest challenge in identity access management is balancing security with developer productivity. If your policies are too restrictive, developers will spend more time filing tickets for access than writing code. If they are too loose, your cloud security posture is non-existent. A practical way to solve this is to embrace 'Just-in-Time' access or elevated privileges that expire automatically. Many teams find success by using IAM conditions, which allow you to grant access based on specific context, such as the time of day, the resource tag, or even the IP address range of the requester.
Recent Job Descriptions
06. References
AWS IAM documentation: AWS IAM documentation
AWS documentation home: AWS documentation home
AWS Well-Architected Framework: AWS Well-Architected Framework
07. Conclusion
Mastering Google Cloud IAM is not about memorizing every role, but about understanding the logic of trust. Start small, use specific roles, and avoid broad permissions at all costs. As you gain more experience, you will see that these controls are not meant to slow you down; they are the guardrails that keep your production environment stable. If you want to dive deeper into how these concepts apply to modern workflows, check out our resources Scoop Labs for more hands-on training. Always keep your configurations minimal, audit your logs regularly, and stay curious about how your cloud environment protects your data. With time, managing identities will become second nature, allowing you to focus on building great features rather than fighting access issues.
Navigate to Address
Scoop Labs
59, 2nd Floor, VLM Towers, 10th Cross Road, 2nd Stage, Padmanabha Nagar, Banashankari, Bengaluru, Karnataka 560070
Get Direction: Banashankari
Submit a Request
Recent Posts


