
Overview: Azure resource groups act as logical containers for your cloud assets. They help you organize, secure, and monitor everything from virtual machines to databases in one place. By grouping related items, you gain better control over billing and access rights. This guide explains how to use these containers effectively in your daily work.
01. Introduction
In the cloud, you rarely work with a single item. A typical application in Microsoft Azure involves a web server, a database, a virtual network, and perhaps a storage account. When you start building these components, keeping track of them becomes a challenge. If you do not organize them properly, you might end up with a messy dashboard where you cannot tell which server belongs to the production environment and which belongs to a testing sandbox.
Resource groups are the primary solution to this management problem. Think of them as folders on your computer, but instead of files, they hold cloud resources. Every resource in Azure must exist inside exactly one resource group. This mandatory structure forces a level of order that is essential for enterprise-level cloud management. When I teach students at our software training center, the first thing I emphasize is that a well-structured resource group saves hours of debugging and billing audits later.
Managing cloud infrastructure requires more than just knowing how to click buttons in the Azure Portal; it requires a mental model of how your resources interact. Beginners often view resources as isolated items, but an experienced engineer sees them as part of a collective. If you build a virtual machine but forget to attach it to a virtual network or a specific resource group, you create a dangling asset that is harder to track. Understanding that these containers are the "home" for your assets is the first step toward professional-grade cloud operations.
The organizational hierarchy of Azure is quite specific. You have management groups at the top, followed by subscriptions, then resource groups, and finally the actual resources like VMs, databases, or web apps. By focusing on the resource group layer, you are effectively controlling the middle-tier of your cloud environment. This is where most day-to-day administrative tasks happen, and mastering it early will make your transition into advanced topics like Infrastructure as Code much smoother.
02. Lifecycle Management Logic
The most practical benefit of using resource groups is the ability to manage the lifecycle of your infrastructure. If you are running a project, you likely have a start and an end date. When the project finishes, you need to clean up all the underlying infrastructure to avoid unnecessary costs. Without a resource group, you would have to delete each virtual machine, network interface, and public IP address individually. This is error-prone and tedious.
By placing all related items into a single resource group, you can delete the entire container at once. Azure takes care of deleting everything inside it, ensuring that no orphaned disks or stale network logs are left behind. This is crucial for environments where resources are spun up and torn down frequently, such as temporary staging areas or training labs. I often see students forget to delete a single disk after a test, and that disk continues to accrue costs long after the server is gone; using resource groups prevents this "ghost resource" syndrome.
Consistent Environment Separation
Separating development, testing, and production environments is a standard industry practice. Using separate resource groups for each tier ensures that your development experiments never interfere with your production database. If a developer accidentally deletes a resource, the impact is isolated to that specific group, leaving your production infrastructure safely untouched.
Think about the last time you were working on a deployment script. If you had to run that script against a production environment, you would be incredibly nervous. By having a separate resource group for "Dev," you create a safety net. You can wipe the dev resource group and recreate it without a second thought. This separation of concerns is exactly how teams move fast while keeping their production environments stable. It transforms the way you approach deployments from a fearful task into a routine, repeatable workflow.
Furthermore, this logic extends to resource dependencies. Often, a web app depends on a specific cache or storage account. When you look at your Azure Portal, you can see these dependencies clearly within the resource group view. If you move a resource out of a group, you might break the connectivity or the management policy applied to that group. Keeping related items together is not just about filing; it is about respecting the architectural relationship between your cloud components.
Placement Clients


MSME Companies in UK & US
03. Permissions and Governance Strategies
Access control is another area where resource groups shine. In a team setting, you might want to give your junior developers access to the development environment but restrict them from touching the production environment. By applying Role-Based Access Control (RBAC) at the resource group level, you grant permissions to the container, and those permissions automatically flow down to every item inside it.
This inheritance model simplifies security audits. Instead of checking permissions for fifty individual items, you only need to verify the policies assigned to the resource group. This helps maintain a clean security posture and ensures that you follow the principle of least privilege. Many professionals entering the industry find that mastering this granular control is a major part of passing certification exams and handling real-world deployments.
Comparing Resource Management Scopes
It is important to understand where resource groups sit in the wider context of Azure hierarchy. While you can set policies at the subscription level, doing so might be too broad for specific project needs. Resource groups provide that "sweet spot" of granularity where you can enforce tags, budget alerts, and access policies without affecting the entire organization's cloud footprint.
| Scope Level | Best Use Case | Granularity |
|---|---|---|
| Subscription | Billing and enterprise limits | Very Low |
| Resource Group | Project lifecycle management | Medium |
| Individual Resource | Specific fine-tuned access | High |
| Management Group | Organization-wide policy enforcement | Very Low |
When you look at this table, notice how the "Resource Group" row represents the bridge between individual resources and your organizational budget. If you are a junior engineer, you might start by just creating resources, but as you grow, you will find yourself dealing more with subscription-level policies. Understanding that the Resource Group is the primary target for your daily security tasks will help you navigate Azure policies with more confidence.
Consider a scenario where you have a specific database that requires higher security than the rest of the web app. You might be tempted to put it in a separate group, but that breaks the lifecycle logic we discussed earlier. Instead, you can keep them in the same group but apply a specific RBAC role at the resource level. This is the beauty of Azure; the hierarchy is flexible enough to handle complex requirements without losing the simplicity of the folder-based model.
04. Resource Group Deployment Patterns
When you start designing your cloud architecture, you need a strategy for how you group items. One popular approach is to group by application lifecycle, where all components for a single app live together. Another approach is to group by location, where you keep all resources in a specific region, such as Central India or US East, in one group. This helps if you have to manage latency or compliance requirements related to data sovereignty.
Regardless of your chosen pattern, consistency is key. Document your naming conventions early. If you name your groups randomly, you will eventually lose track of what is inside them. I always advise juniors to include the environment name and the project name in the resource group tag, such as dev-web-app-rg or prod-db-service-rg. This small detail makes monitoring and reporting much easier as your infrastructure scales.
Avoiding Common Configuration Traps
One common mistake is putting too many unrelated items into a single resource group. This creates a blast radius issue; if you need to perform an action on that group, you might affect things you did not intend to touch. Conversely, creating a new resource group for every single tiny resource makes it impossible to track costs or manage permissions efficiently. Aim for a balanced approach where the resources in a group share a common purpose or lifecycle.
Another trap is ignoring tagging. Many teams rely solely on the resource group name for organization, but tags allow you to query your resources across different groups. For example, if you tag every resource with "CostCenter: Marketing," you can generate a report for the marketing department even if their resources are spread across five different resource groups. This cross-group visibility is a life-saver during end-of-month billing reviews when managers ask why their budget is trending upwards.
Finally, avoid the temptation to move resources across groups frequently. While Azure allows you to move resources, it can be tricky if those resources have strict dependencies or hard-coded network references. Always plan your resource group structure during the design phase. If you are building a new application in our DevOps course, take ten minutes to map out your resource group naming convention before you deploy your first virtual machine. It pays off immediately.
05. Lifecycle Management Through Resource Group Boundaries
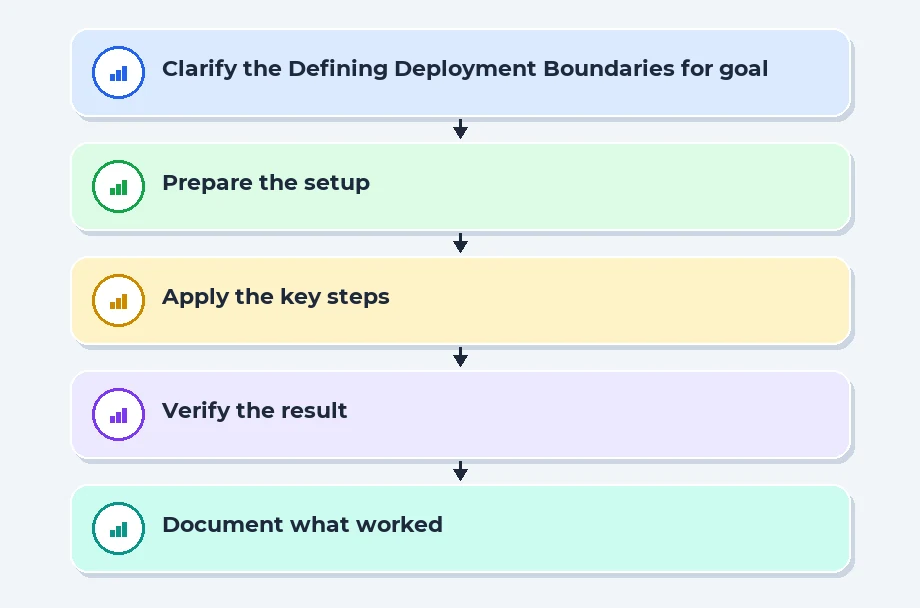
The most practical way to view a resource group is as a container for a shared fate. When you group a web application, its database, and its storage account together, you aren't just filing away digital assets; you are defining the atomic unit of your deployment lifecycle. In a professional environment, this structure prevents the dreaded scenario where a developer deletes a virtual machine only to realize later that they accidentally orphaned a critical managed disk or a network security group. By binding these resources to a single lifecycle, you ensure that when the development project concludes, the cleanup process is surgical rather than speculative.
Think of it like a folder on your computer desktop containing everything needed for a specific client presentation. If you decide to remove that project, you don't hunt through your entire hard drive for scattered files. You move the folder to the trash, and everything associated with that work vanishes at once. Azure resource groups apply this exact logic to cloud infrastructure. This approach minimizes the risk of "cloud sprawl," where forgotten services continue to rack up costs long after their intended purpose has expired. It forces a mindset of accountability, where every resource must justify its existence within the context of a parent group.
Defining Deployment Boundaries for Production Safety
Beyond simple cleanup, resource groups serve as the primary sandbox for enforcing deployment policies. You can apply Azure Policy at the resource group level to ensure that every asset within that group adheres to specific compliance requirements, such as regional restrictions or naming conventions. If you have a group designated for high-security data, you can restrict access so that only specific service principals can interact with it, creating a blast radius that is contained, manageable, and highly auditable.
When you shift to an automated deployment pipeline, the resource group becomes your target destination. By using Infrastructure as Code tools like Terraform or Bicep, you deploy your entire stack directly into a specific group. If a deployment goes sideways, you don't have to troubleshoot individual components. You can simply redeploy the entire group or roll back the state, knowing exactly which resources were modified. This modularity allows your team to iterate on microservices independently, as you can spin up a temporary resource group for a feature branch, test it thoroughly, and then destroy the entire environment without touching your stable production resource group.
Recent Job Descriptions
06. References
Azure Resource Manager Documentation: Manage Resource Groups
NIST Cloud Computing Standards: NIST Cloud Computing
Cloud Security Alliance Research: CSA Research
07. Conclusion
Understanding resource groups is foundational for anyone building on Azure. These logical containers do more than just hold files; they form the backbone of your security, billing, and lifecycle management strategies. By practicing with these groups in your professional projects, you learn to think like an architect rather than just a user. As you gain more experience, you will find that a well-planned resource structure is one of the most effective ways to keep your cloud footprint organized and secure.
Navigate to Address
Scoop Labs
59, 2nd Floor, VLM Towers, 10th Cross Road, 2nd Stage, Padmanabha Nagar, Banashankari, Bengaluru, Karnataka 560070
Get Direction: Banashankari
Submit a Request
Recent Posts


