
Overview: Azure networking is the foundation for how cloud services talk to each other. By using Virtual Networks (VNet), you create isolated spaces for your resources to communicate securely. This guide explains how these networks work, how data flows between them, and how you can manage these connections to build reliable cloud infrastructure in your projects.
01. Introduction
When I mentor students, the most common hurdle they face is understanding that a cloud network is not just a digital version of a physical switch. In the Azure ecosystem, networking is defined by software. Every resource, from a virtual machine to a database, lives inside a Virtual Network, or VNet. Think of a VNet as your own private plot of land in the shared cloud neighborhood.
You control who enters and leaves this space. Without proper configuration, your services would be invisible to each other or, worse, exposed to the entire internet. Understanding these basics is critical for anyone pursuing an Azure Course. We will break down how these resources actually signal each other and why your design choices matter for long-term scalability. Cloud computing requires a fundamental shift in how you think about connectivity, moving away from cables and hardware to identity-based and policy-based traffic control.
Learning to architect these networks is a professional rite of passage. In my experience, those who grasp the VNet concepts early on tend to move faster into DevOps and cloud engineering roles. If you are aiming for placement assistance in high-growth companies, showing you can design a secure, segmented VNet architecture is often the deciding factor in a technical interview. Let us start by looking at how your resources actually talk to one another once they are placed inside their virtual homes.
02. How Virtual Networks Manage Resource Traffic
Inside a VNet, resources communicate using private IP addresses. These addresses are invisible to the public internet, which provides an inherent layer of security. When you launch two virtual machines in the same subnet, they can talk to each other immediately by default. This internal routing is managed by the Azure fabric, which acts as the invisible glue connecting your components. It is important to realize that the fabric is not something you configure; it is the underlying platform that ensures your packets reach their destination.
However, real-world applications rarely stay in one subnet. You might have a web server layer that needs to talk to a backend database. This is where Network Security Groups (NSGs) become essential. You can think of an NSG as a gatekeeper. You define rules that allow or deny specific traffic based on the source, destination, and port. If you are currently working on a Full Stack with Gen AI project, you have likely dealt with blocked requests. Usually, the issue is not the code, but an NSG rule that is being too strict or not strict enough for the traffic you are trying to send.
Subnet Segmentation Strategies
Segmentation is the practice of splitting your VNet into smaller, isolated zones. A common architectural pattern involves placing web servers in a public subnet and databases in a private subnet. By isolating the database, you ensure that even if the web server is compromised, the data remains tucked away from direct external access. This is the first step toward a "zero trust" architecture.
Proper segmentation also helps in monitoring. When traffic stays within the same VNet, latency is negligible. But if you need to enforce strict compliance, such as PCI-DSS, you will use subnets to apply different security policies to different tiers of your application. This modular approach is something we emphasize heavily during Software Testing training, as it allows for cleaner testing boundaries where you can verify the behavior of one tier without impacting the availability of others.
Address Space Allocation
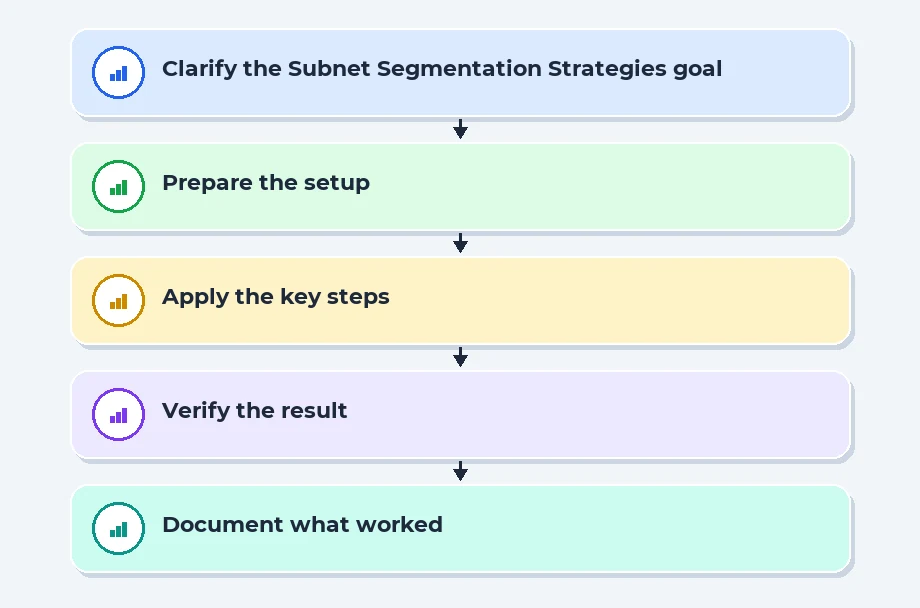
When defining a VNet, you must specify a CIDR block. Beginners often pick an arbitrary range without thinking about future growth. I always advise my students to choose a range that leaves plenty of room for expansion. If you define a range that is too small, you cannot simply "expand" it later without significant headache. It is like trying to add a room to a house after the foundation is already poured.
Once you define your main address space, you then carve that into subnets. This hierarchical planning is vital. You should never overlap address spaces if you plan to connect multiple VNets together through peering. If your development environment uses 10.0.0.0/16 and your production environment also uses 10.0.0.0/16, you will face routing nightmares when you try to link them. Always document your IP planning before you click 'create'.
Placement Clients


MSME Companies in UK & US
03. Navigating Connectivity Options for Hybrid Cloud
Sometimes your cloud resources need to reach out to your local office servers. Azure provides several ways to bridge this gap. A Site-to-Site VPN is the most common choice, using an encrypted tunnel over the public internet to connect your on-premises network to your Azure VNet. It is cost-effective and relatively quick to set up for smaller teams or regional branch offices.
For enterprises requiring high performance and consistent bandwidth, ExpressRoute is the preferred path. Unlike a VPN, ExpressRoute provides a private, dedicated connection that does not traverse the public internet. This reduces the risk of packet loss and provides a much more stable environment for latency-sensitive applications like real-time financial trading systems or large-scale data synchronization. While it costs significantly more, the predictability it offers is often worth the premium for production workloads.
Comparing Connectivity Methods
Choosing the right connection depends on your budget and data requirements. Below is a quick comparison of the most popular methods used by infrastructure teams.
| Method | Security Level | Typical Use Case | Latency |
|---|---|---|---|
| Site-to-Site VPN | High (Encrypted) | Small to mid-sized offices | Variable |
| Point-to-Site VPN | High (Encrypted) | Remote developer access | Variable |
| ExpressRoute | Very High (Private) | Mission-critical production | Low/Stable |
| Public Internet | Low | Testing/Dev environments | High/Unstable |
Peering and the Hub and Spoke Model
When you have multiple VNets, you need a way for them to talk to each other. Virtual Network Peering is the standard mechanism here. It allows resources in one VNet to talk to another as if they were in the same network. However, peering is not transitive. If VNet A is peered to VNet B, and B is peered to C, A cannot automatically talk to C without further configuration.
This limitation leads us to the Hub and Spoke model. You designate one VNet as the 'Hub'-this is where your shared services like firewalls, VPN gateways, and monitoring reside. All your 'Spoke' VNets connect back to this hub. This creates a centralized control point for all your traffic. It makes auditing much easier because you are checking one set of logs in the hub rather than trying to manage security policies in ten different spokes.
04. Common Mistakes When Configuring Azure Networking
One of the most frequent errors I see in student projects is over-provisioning public IPs. Beginners often assign a public IP address to every single virtual machine, which significantly increases the attack surface. In a professional environment, you should only expose a Load Balancer or an Application Gateway to the internet, keeping all other back-end services on private addresses. If a machine does not need to be reachable from the internet, it should not have a public IP.
Another common oversight is failing to properly plan IP address ranges. If you define a VNet range that is too small, you will eventually run out of addresses as you scale your infrastructure. Expanding a VNet later is possible, but it can be messy and might require re-architecting your entire network. Always start with a larger CIDR block than you think you need. It costs nothing to have a larger range that you are not using, but it costs hours of downtime to fix a range that is too small.
Debugging Connection Failures
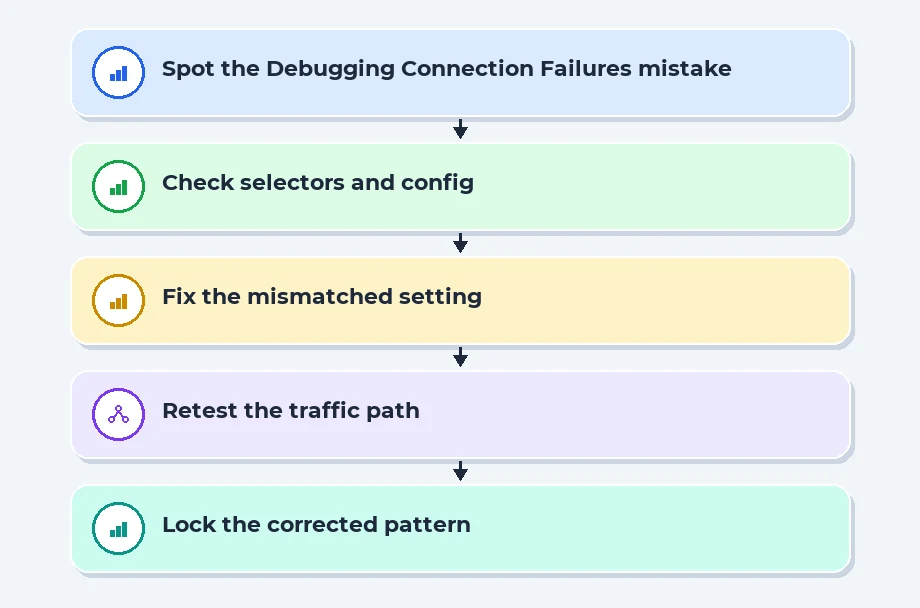
When resources cannot communicate, the first instinct is to blame the code. Usually, it is a network rule. Azure provides a tool called Network Watcher that is invaluable for troubleshooting. It allows you to run a connection verify check, which tells you exactly which rule is blocking the traffic. This tool saved me countless hours back when I was managing large-scale deployments.
If you are working on a Full Stack MERN Course, you will likely encounter these issues when trying to connect your front-end container to a database service. Instead of guessing, check your NSG logs and the effective security rules on your network interface. This logical, systematic approach to debugging-checking the route table, checking the NSG, and then verifying the application port-is what separates a junior developer from a lead engineer. Do not just look at the code; look at the pipes the code travels through.
Neglecting NSG Governance
Many teams treat Network Security Groups like a "set and forget" feature. They add an 'allow all' rule while debugging and then forget to remove it. This is a massive security risk. I always recommend using a naming convention for your rules (e.g., 'Allow-Web-To-DB-Port-5432') so that when you audit them six months later, you know exactly why that rule exists.
If you use Infrastructure as Code, like Terraform or Bicep, you can version-control your networking rules. This is the gold standard. When you need to change a firewall rule, you submit a pull request, have it reviewed, and then deploy it. This prevents the 'manual clicker' syndrome where someone changes a setting in the portal, breaks production, and no one knows who did it or how to roll it back. Networking is software, and it should be treated with the same rigor as your application logic.
05. Managing Traffic Flow with Network Security Groups
Once your Virtual Networks are connected, the real work begins: deciding who gets to talk to whom. In the physical world, this is like having a security guard at the lobby desk of an office building. In Azure, that guard is the Network Security Group, or NSG. Think of an NSG as a set of rules that you attach to a network interface or a subnet. Without these rules, your resources might be wide open to the entire internet, which is a recipe for disaster. You define these rules using five-tuple information: source, source port, destination, destination port, and protocol. If a packet tries to come in from an unknown IP address on a suspicious port, the NSG looks at your list, sees no permission, and drops the traffic instantly.
The beauty of the NSG approach is that you can be incredibly granular. You might have a web server that needs to accept traffic from the public on port 443, but you definitely don't want that same server talking to your internal database on port 1433. By applying specific rules, you create a "least privilege" environment where even if a resource is compromised, it cannot easily pivot to sensitive areas of your infrastructure. It is easy to get overwhelmed by complex firewall setups, but starting with the default "allow all inbound, deny all outbound" mindset is a trap. Always flip the script: deny everything by default and only open the specific holes you absolutely need for your application to function.
The Art of Rule Priority and Evaluation
One common mistake I see junior engineers make is forgetting that NSG rules are evaluated in a specific order based on priority numbers. Azure processes these rules starting from the lowest number-like 100-and works its way up to 65500. The moment a packet matches a rule, the evaluation stops. If you accidentally create a rule with priority 100 that allows all traffic, it doesn't matter if you have a hundred restrictive rules with higher priority numbers underneath it; the traffic is already through. This is why keeping your rule list lean and organized is critical for long-term sanity.
When troubleshooting communication issues, always check the "Effective Security Rules" blade in the Azure portal. It shows you exactly what is happening to a packet as it hits your virtual machine, factoring in all the rules that apply to that specific resource. If you think your rules are correct but traffic is still failing, it is usually because a higher-priority rule is catching the traffic first, or a different network component like an Application Gateway is intercepting the flow before it even hits your NSG. Keep your priority numbers spaced out-use increments of 100-so you have room to insert new, more specific rules later without having to renumber your entire security policy.
Recent Job Descriptions
06. References
MDN Web Docs:MDN Web Docs
OWASP - Web security resources:OWASP - Web security resources
NIST Cybersecurity Framework:NIST Cybersecurity Framework
07. Conclusion
Azure networking is less about memorizing every button and more about understanding the flow of data. By mastering the concepts of subnets, NSGs, and connectivity models, you gain the ability to design systems that are both secure and performant. Whether you are building a simple web app or a complex hybrid infrastructure, the principles remain the same. Keep your networks isolated, audit your traffic rules regularly, and always design for scale. With practice, you will find that these networking components become second nature, allowing you to focus on writing better code and delivering value. The best network is one you understand deeply enough to troubleshoot without panic.
Navigate to Address
Scoop Labs
59, 2nd Floor, VLM Towers, 10th Cross Road, 2nd Stage, Padmanabha Nagar, Banashankari, Bengaluru, Karnataka 560070
Get Direction: Banashankari
Submit a Request
Recent Posts


